- Human Verified
- Production Readiness
- Audits
Independent Technical Audits for Software Products
Vibecop reviews AI-generated / vibe-coded and legacy applications for security, architecture, scalability, reliability, and production readiness before you ship, scale, or raise.
Adult supervision for AI-built and fast-built products.
Founders ship fast with Claude Code, Lovable, Bolt, and Cursor. Enterprise platforms surface risks at scale. But architecture, security, and production decisions still need real senior engineering judgment. Vibecop is the human verification layer.


How an Audit Runs, Stage by Stage
Machine-speed analysis, senior engineer verification, and a roadmap your team can execute every stage accounted for.
Intake
Day 0
Scope & Access
Day 0
Intake
You share the repo, the stack, and what ships next. We scope the audit against your actual launch risk, not a generic checklist.
Analysis
Automated
Codebase Analysis
Automated
Analysis
Intelligent automated analysis across your architecture, codebase, infrastructure config, and security posture, surfacing patterns, risks, and structural issues at machine speed.
Verification
Human
Senior Engineer Review
Human
Verification
Every finding is reviewed and validated by senior engineers. Context matters. We separate critical risks from noise, turning automated signals into decisions you can trust.
Roadmap
Delivered
Prioritized Risk Roadmap
Delivered
Roadmap
A clear, actionable plan ordered by severity and business impact. No vague recommendations. Specific fixes your team can execute immediately.
Support
Ongoing
Strategic Implementation Support
Ongoing
Support
We stay on to oversee execution, advise on architecture decisions, or provide CTO-level oversight as your product scales.


The 3-7 Business Day Production Readiness Plan
Typical scope-to-handoff time in business days. Larger or more tangled codebases run longer, and we tell you which side of the window you are on up front.
Day 0: Scope & Access
We map your repo, your stack, and what ships next. The audit is scoped against your actual launch risk, not a generic checklist.
Days 1-2: Automated Analysis
Machine-speed analysis across architecture, codebase, infrastructure config, and security posture. Every structural risk and anti-pattern gets surfaced.
Days 3-5: Senior Engineer Verification
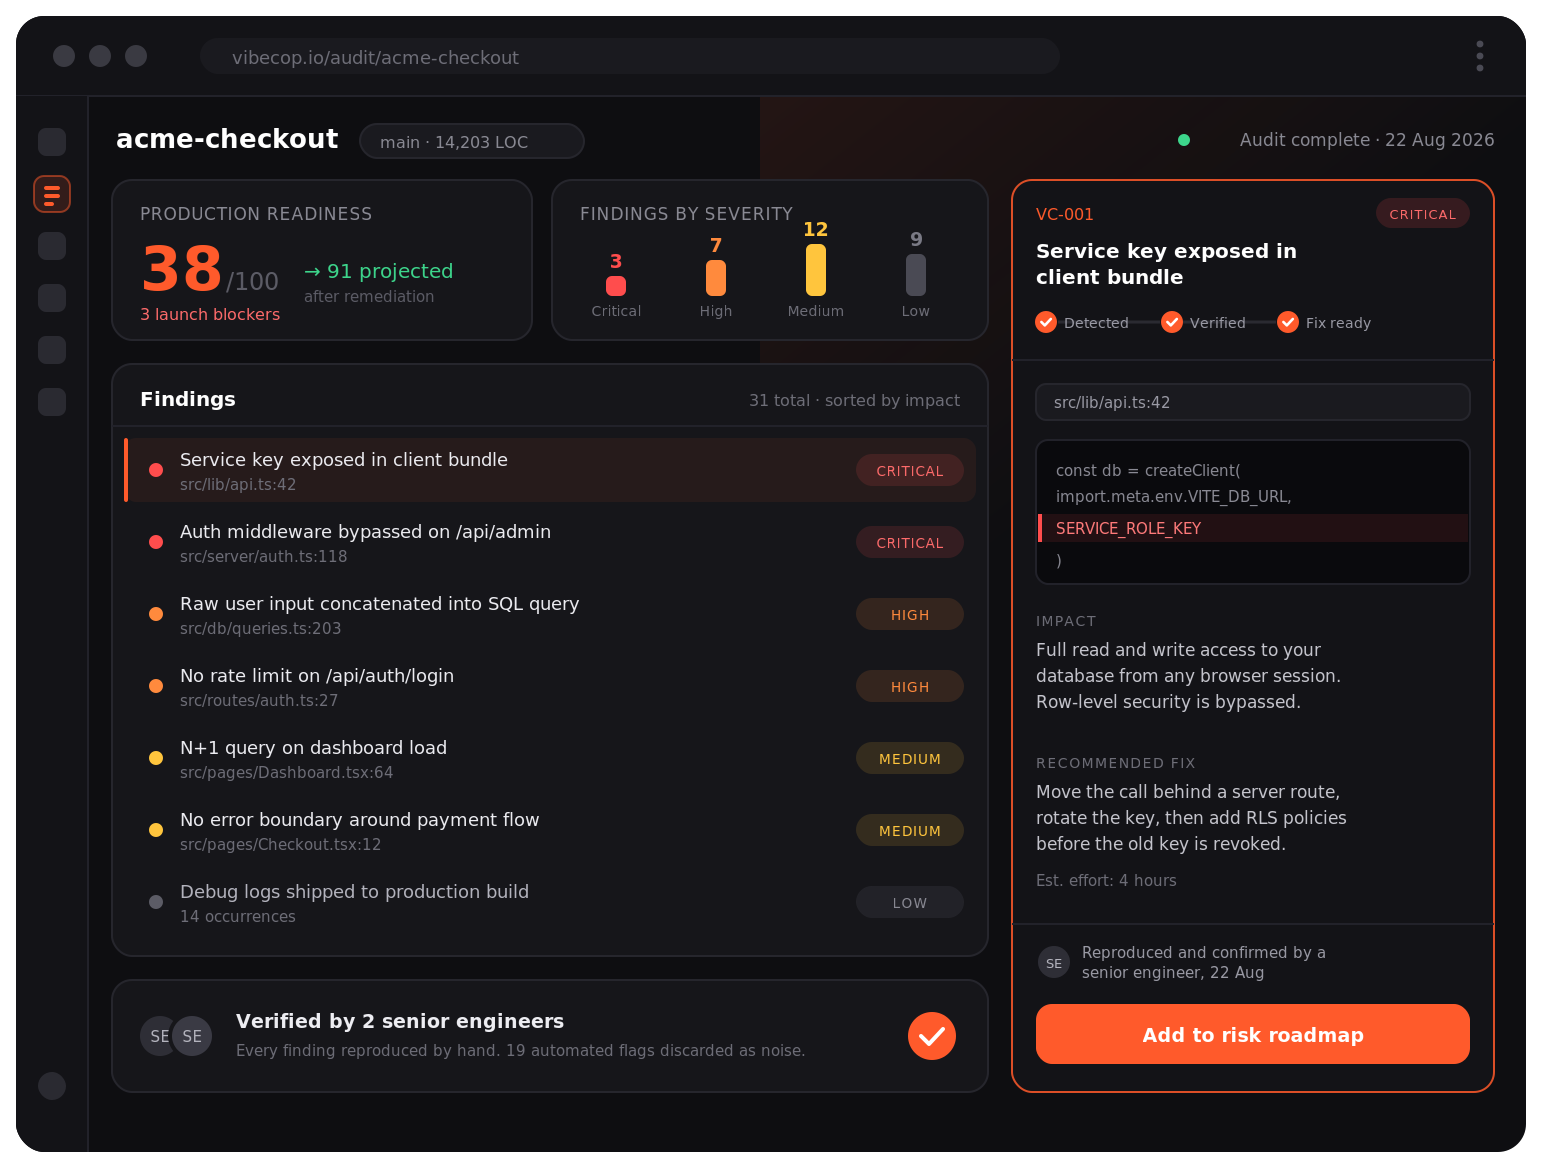
Every finding is reproduced and validated by hand. False positives cut, severity assigned against your business context rather than a CVSS score in isolation.
By day 7: Risk Roadmap Handoff
A prioritized fix list your team can execute, walked through live with the engineer who wrote it.
What Stack Are You On?
We review modern SaaS and AI-focused stacks in place no migration, no rewrite required.
Integration
- REST APIs
- Webhooks
- OAuth
Codebase
- GitHub
- GitLab
- Bitbucket
Deployment
- Heroku
- AWS
- Docker
Scoped Engagements, Priced Up Front
Fixed-scope audits and sprints. One prevented incident typically covers the cost many times over.
Vibecop Focused Audit
From$450
Diagnose one critical workflow
- One agreed workflow traced end to end
- UI, API, database & third-party service tracing
- Root-cause diagnosis of the reported problem
- Verified issues vs. hypotheses
- Severity & affected code areas
- Actionable fix plan with acceptance checks
- Developer walkthrough
Vibecop Lite Audit
From$1,200
Find the risks sitting in the code
- Full codebase review
- Security & access-control assessment
- Dependency & supply-chain risk check
- Secrets & configuration exposure scan
- Error handling & input validation review
- Code quality & maintainability findings
- Human-verified, evidence-backed findings
- Prioritized fix list
Vibecop Full AuditFeatured
From$2,900
Know exactly what you’re shipping
- Everything in the Lite Audit
- Architecture & data-flow review
- Third-party integrations & APIs
- Cloud & infrastructure review
- Database & background jobs
- AI/LLM & agent risk review
- Production-readiness & deployment review
- Performance & scalability analysis
- Prioritized roadmap & executive report
- Penetration testing add-on (scoped separately)


Confidence Package
Ship knowing the code and the user journeys both hold up.
From$3,500$3,900
Save $400 · 10–15 business days
Full Audit
- Architecture & data flows
- Integrations & APIs
- Cloud & infrastructure
- Prioritized roadmap & executive report
Essential QA
- Critical user journeys
- Sign-in, permissions & input validation
- Browser & mobile checks
- Defect log with evidence
Plus one joint findings walkthrough with combined priorities
Final pricing depends on codebase size (lines of code) and complexity, agreed before work begins.
Human Verification, Not Just a Scan
Automated tools surface signals. Senior engineers decide what matters, why it matters, and what to do next.
Typical audit turnaroundScope to roadmap
3–7 business days
Verified by a senior engineerHuman verified
Every finding
Shipped without human reviewWhat we accept
No findings
Frequently Asked Questions
Clear, straightforward answers about our process, security, and support.
Yes. Vibecop works with private repositories and sensitive production systems under secure review workflows and NDA-friendly processes.
Build with
confidence.
AI builds the product. Vibecop makes sure it won’t break in production, fail under scale, or expose your users to risk. One audit. Fewer expensive surprises.